Microsoft Entra Password Writeback Failure: Troubleshooting SSPR, Event IDs, AdminSDHolder & TLS Gotchas
Deploying Self-Service Password Reset (SSPR) in Microsoft Entra ID (formerly Azure AD) is a major milestone for enterprise IT helpdesks. Users can reset their forgotten passwords from a web browser or the Windows login screen without calling support. However, in hybrid environments where Active Directory Domain Services (AD DS) remains the authoritative identity source, this process depends entirely on Password Writeback.
When Password Writeback fails, the user experience collapses. An employee successfully verifies their MFA in the cloud, enters a new password, and is greeted with a cryptic failure: “We’re sorry, but we cannot reset your password at this time. This may be due to an administrative policy.” Meanwhile, directory administrators are left sifting through obscure event logs on the Entra Connect server.
User resets password in Entra Cloud (HTTPS) ➔ Azure Service Bus Relay (Outbound TLS 443) ➔ Entra Connect Sync Engine (ADSync / Cloud Sync Agent) ➔ Kerberos / Netlogon RPC ➔ On-Premises Domain Controller (LSASS / SAM)
How Password Writeback Actually Works Under the Hood
Many systems engineers assume that Password Writeback requires opening inbound firewall ports to internal Domain Controllers. In reality, Microsoft engineered Password Writeback to operate purely over outbound connections using the Azure Service Bus Relay:
──(MFA Verified)──►
Entra ID SSPR Service
──(Encrypted Session)──►
Azure Service Bus Relay (*.servicebus.windows.net)
──(Outbound Polling TLS 443)──►
Entra Connect Server
──(SetPassword RPC API)──►
On-Premises Domain Controller
The Core Event IDs: Reading the Application Event Log
When troubleshooting writeback, stop guessing and inspect the Application Log on the server running Microsoft Entra Connect. Filter by event source Directory Synchronization or PasswordResetService:
| Event ID | Error Meaning | Primary Root Cause |
|---|---|---|
| Event ID 31008 | Password reset failed: hr=80070005 (Access is denied) |
AdminSDHolder inheritance broken on the user object, or missing permissions on the AD DS Connector account. |
| Event ID 31011 | Password reset failed: hr=800708c5 (Password policy violation) |
The password met Entra cloud rules, but violated on-premise Default Domain Policy or a Fine-Grained Password Policy (PSO). |
| Event ID 31005 | Cannot establish connection to Service Bus Relay | Perimeter firewall or proxy performing SSL/TLS decryption on *.servicebus.windows.net, breaking mutual certificate pinning. |
| Event ID 31012 | Password reset failed: hr=80070525 (Account disabled/locked) |
The user account is disabled, or account lockout policy prohibits resets while locked. |
The #1 Cause: AdminSDHolder & Broken Inheritance (Event ID 31008)
By far the most common failure in production environments involves privileged users or users who previously belonged to protected groups. When an administrator attempts to reset their password via SSPR, the server returns hr=80070005 (Access is denied).
The Protected Group Mechanism
Windows Active Directory runs a background system thread every 60 minutes called SDPROP (Security Descriptor Propagator). SDPROP scans all objects belonging to protected groups (e.g., Domain Admins, Enterprise Admins, Schema Admins, Account Operators, Backup Operators):
- It strips off all inherited permissions from parent Organizational Units (OUs).
- It disables the “Include inheritable permissions from this object’s parent” checkbox.
- It overwrites the Access Control List (ACL) with the template from the
CN=AdminSDHolder,CN=System,DC=domain,DC=comcontainer.
Because the Entra Connect sync account (typically named MSOL_xxxxxxxxxxxx) only has permissions granted at the root of the OU or domain, SDPROP strips its ability to reset the user’s password!
How to Fix Broken Inheritance with PowerShell
To check if an affected user has broken permission inheritance, run:
# 1. Check if inheritance is disabled
$user = Get-ADUser -Identity "jdoe" -Properties "nTSecurityDescriptor"
$user.nTSecurityDescriptor.AreAccessRulesProtected

# If Output returns True, inheritance is blocked by AdminSDHolder!

# 2. Re-enable permission inheritance on the user object
$acl = Get-Acl -Path "AD:$($user.DistinguishedName)"
$acl.SetAccessRuleProtection($false, $true)
Set-Acl -Path "AD:$($user.DistinguishedName)" -AclObject $acl

# 3. Verify the user is not actively inside a protected group
Get-ADPrincipalGroupMembership -Identity "jdoe" | Select-Object Name
Security Architecture Best Practice: Never synchronize high-privilege administrators (Enterprise Admins, Domain Admins) to Microsoft Entra ID. Cloud administrators should use cloud-only accounts (e.g., admin.jdoe@contoso.onmicrosoft.com) protected by Conditional Access and FIDO2 keys.
The #2 Cause: Fine-Grained Password Policy (FGPP) Mismatches (Event ID 31011)
A classic operational pitfall occurs when cloud password policies differ from on-premises Active Directory policies.
The Disconnect:
- By default, Microsoft Entra ID enforces an 8-character minimum password length without strict complexity requirements.
- Your on-premises Active Directory Default Domain Policy or Fine-Grained Password Policy (PSO) might enforce a 14-character minimum, history requirement (cannot reuse last 24 passwords), or a minimum password age (cannot change password more than once per 24 hours).
When the user resets their password in the cloud, Entra ID approves the 10-character password. However, when the Entra Connect engine attempts to apply it via RPC to the local DC, LSASS rejects the update with ERROR_PASSWORD_RESTRICTION (0x800708c5), logging Event ID 31011.
Auditing the Effective Policy via PowerShell
To find the exact policy governing the user on-premises:
# Query the effective password policy for the user (including PSOs)
Get-ADUserResultantPasswordPolicy -Identity "jdoe" | `
  Select-Object Name, MinPasswordLength, ComplexityEnabled, `
                PasswordHistoryCount, MinPasswordAge, MaxPasswordAge
The Fix: Deploy Microsoft Entra Password Protection on-premises. By installing the Entra Password Protection proxy and DC agents, your on-premises DCs will enforce the same global banned password list and custom tenant dictionaries used in the cloud, unifying password policy enforcement.
The #3 Cause: TLS Decryption & Proxy Failures (Event ID 31005)
If Password Writeback fails globally for every single user in the organization, the issue is almost certainly network transport.
The Entra Connect Password Writeback service establishes a persistent, long-lived outbound TLS socket to Azure Service Bus Relay over TCP port 443. Common network culprits include:
- SSL / TLS Deep Packet Inspection: Perimeter firewalls (Palo Alto, Fortinet, Zscaler, Cisco ASA) intercepting HTTPS traffic and presenting a corporate firewall certificate. The Entra Connect client relies on mutual certificate pinning; if the TLS certificate is rewritten, the connection drops immediately with Event ID 31005.
- Missing Service Bus FQDN Whitelist: Ensure the following outbound wildcard endpoints are exempted from proxy authentication and SSL decryption:
*.servicebus.windows.net
*.msappproxy.net - Enforcing TLS 1.2 on the Operating System: Ensure modern secure channel protocols are active on the Entra Connect Windows Server:
# Force TLS 1.2 in .NET Framework
Set-ItemProperty -Path 'HKLM:\SOFTWARE\Microsoft\.NETFramework\v4.0.30319' -Name 'SchUseStrongCrypto' -Value 1 -Type DWord
Set-ItemProperty -Path 'HKLM:\SOFTWARE\Wow6432Node\Microsoft\.NETFramework\v4.0.30319' -Name 'SchUseStrongCrypto' -Value 1 -Type DWord
Granting the Required Active Directory Permissions
If you re-installed Entra Connect or created a custom service account, verify that the MSOL_ sync account possesses the explicit rights required for writeback across all user Organizational Units:
- Open Active Directory Users and Computers (
dsa.msc). - Ensure View ➔ Advanced Features is enabled.
- Right-click your Target User OU (or the root domain) ➔ Properties ➔ Security ➔ Advanced.
- Locate the
MSOL_xxxxxxxxxxxxaccount and verify it has:- Reset Password
- Write lockoutTime
- Write pwdLastSet
Need Expert Assistance Securing Hybrid Active Directory & Entra ID?
Our Microsoft-certified directory architects specialize in multi-forest Entra Connect consolidation, migrating from Entra Connect to Cloud Sync, resolving mass attribute collisions, and designing secure hybrid identity infrastructure.
Frequently Asked Questions (FAQ)
Why does SSPR fail with “Access is denied” (Event ID 31008) for domain administrators?
This is caused by the Active Directory AdminSDHolder mechanism. Members of protected groups have their inheritance stripped hourly by SDPROP. The Entra Connect sync account only has permissions inherited from the OU root, so it loses the rights to reset the administrator’s password. Best practice is to use cloud-only accounts for administrative tasks.
Does Password Writeback require inbound firewall ports to be open?
No. Password Writeback operates entirely over outbound connections on TCP port 443. The on-premises Entra Connect server initiates and maintains a long-lived outbound TLS connection to the Azure Service Bus Relay (*.servicebus.windows.net) to listen for password change requests.
What is the difference between Event ID 31011 and Event ID 31008?
Event ID 31008 indicates an Active Directory permissions failure (Access is Denied) on the sync account. Event ID 31011 indicates a password policy violation (such as password complexity, minimum length, or password history restriction) enforced by on-premises domain policies or Fine-Grained Password Policies (PSOs).
Can a user unlock their on-premises account using Entra SSPR without changing their password?
Yes. In the Microsoft Entra Admin Center under Password Reset ➔ On-premises integration, you can enable the option: “Allow users to unlock accounts without resetting their password”. For this to work, the on-premises sync account must have the “Write lockoutTime” permission granted on the user OU.
Related Active Directory & Hybrid Identity Guides
- Microsoft Entra Connect Sync Errors: Fixing Duplicate ProxyAddresses & ImmutableID Mismatches
- Entra Connect vs Cloud Sync: When to Stay, When to Migrate
- Authoritative vs. Non-Authoritative Active Directory Restore: Complete Guide
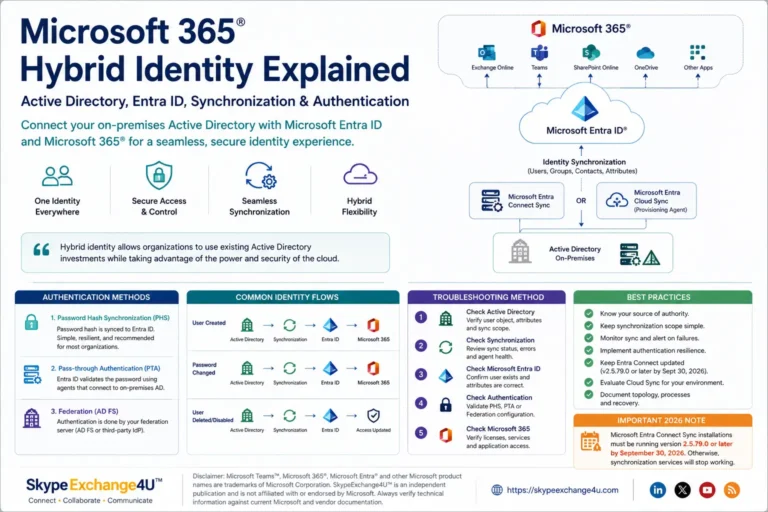
- Types of Active Directory Synchronization with Microsoft Entra ID
- How to Troubleshoot Active Directory Replication: 10 Common Errors & Fixes
- DCDIAG Explained: 15 Active Directory Health Checks Every Admin Should Run